

معرفی و ارزیابی کتاب
Fuzzing for Software Security Testing and Quality Assurance
Ari Takanen;Jared D. DeMott;Charles Miller
English
Beginner
مهندسی نرمافزار
4.6 / 5
0 نظر
2018
سال انتشار
345
صفحه
196
بازدید
Fuzzing for Software Security Testing and Quality Assurance gives software developers a powerful new tool to build secure, high-quality software, and takes a weapon from the malicious hackers' arsenal. This practical resource helps developers think like a software cracker, so the
پیش از خواندن
این کتاب چه چیزی به شما میدهد؟
Fuzzing for Software Security Testing and Quality Assurance gives software developers a powerful new tool to build secure, high-quality software, and takes a weapon from the malicious hackers' arsenal. This practical resource helps developers think like a software cracker, so they can find and patch flaws in software before harmful viruses, worms, and Trojans can use these vulnerabilities to rampage systems. Traditional software programmers and testers learn how to make fuzzing a standard practice that integrates seamlessly with all development activities. The book progresses through each phase of software development and points out where testing and auditing can tighten security. It surveys all popular commercial fuzzing tools and explains how to select the right one for a software development project. The book also covers those cases where commercial tools fall short and developers need to build their own custom fuzzing tools.
از این کتاب بپرس
پرسشت با عنوان و نویسنده همین کتاب برای دستیار ارسال میشود. هر پاسخ ۲ امتیاز مصرف میکند.
وارد شوید تا بتوانید از دستیار کتاب بپرسید.
نظر خوانندگان
0 نظر، میانگین 4.6 از ۵
هنوز نظری ثبت نشده
اگر این کتاب را خواندهاید، تجربهتان را با دیگران به اشتراک بگذارید.
نظر خودت را بنویس
وارد شوید تا نظر خود را ثبت کنید.
پرسش و پاسخ خوانندگان
سؤال مشخص بپرس و از تجربه جامعه استفاده کن.
وارد شوید تا سؤال بپرسید یا پاسخ بدهید.
هنوز پرسشی ثبت نشده
اولین سؤال روشن و مفید را شما مطرح کنید.
بعد از این چه بخوانم؟
منابع مرتبط برای ادامه همین مسیر.
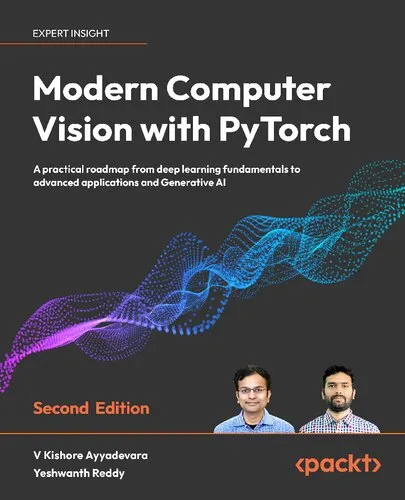
Modern Computer Vision with PyTorch: A Practical Roadmap From Deep Learning Fundamentals to Advanced Applications and Generative AI, 2nd Edition
V Kishore Ayyadevara,Yeshwanth Reddy
2023
مشاهدهٔ کتاب